Three days with the GRC crowd — and they asked the hard questions.
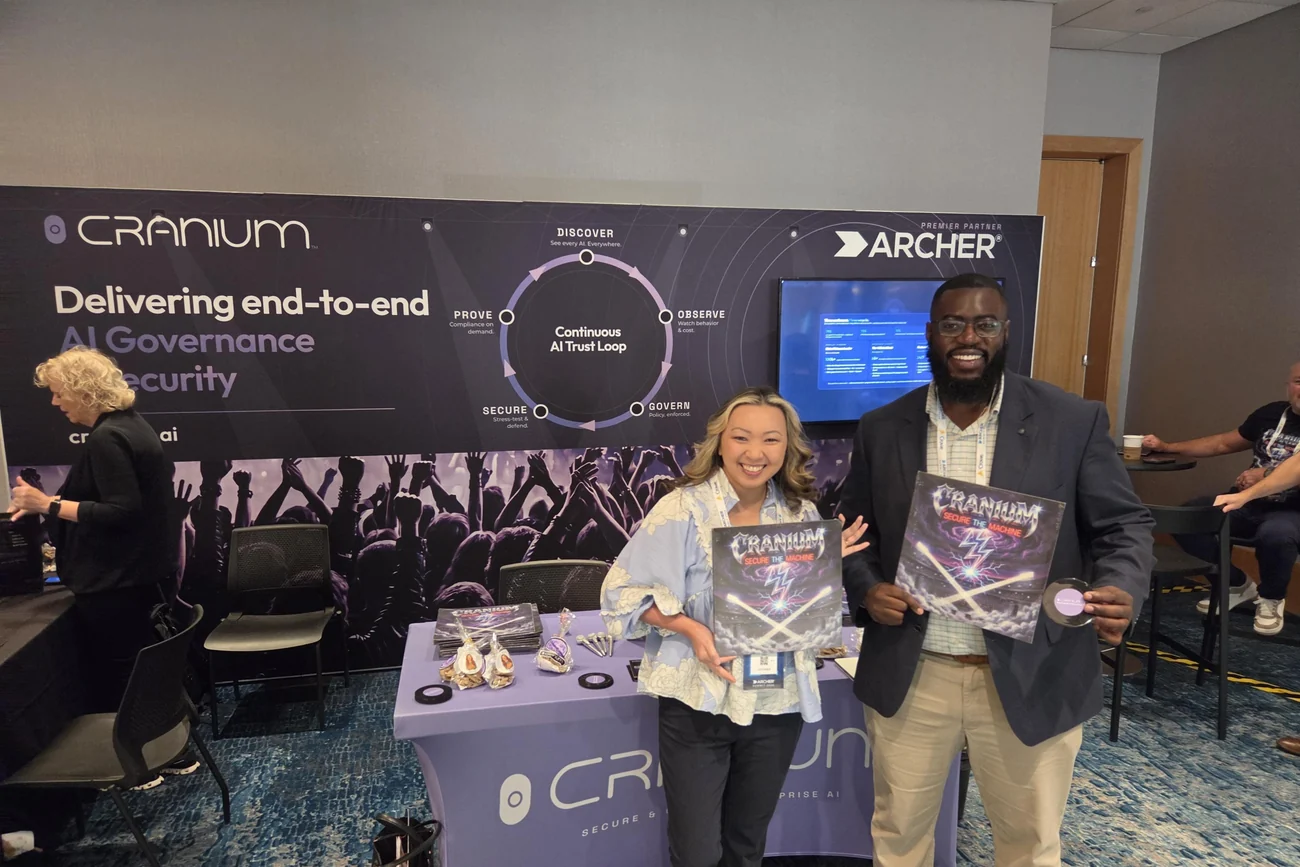
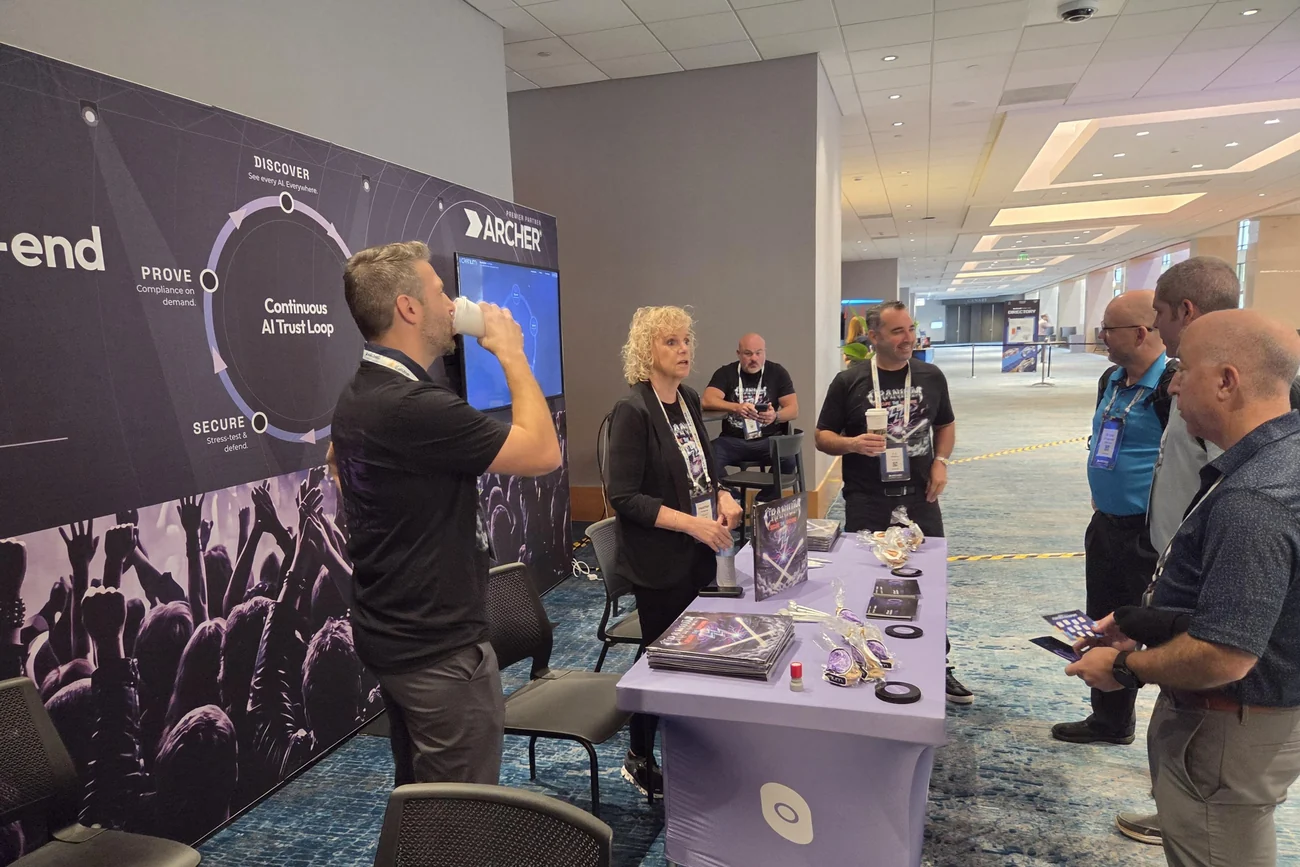
A thousand risk and compliance leaders, three days, and one question behind every conversation: can you prove it? Here’s what we ran on the floor.
AI policy mapped to NIST AI RMF, the EU AI Act and ISO 42001 — defined, enforced and scored continuously rather than once a year. The GRC room did not need that explained twice.
Posture, red-team findings and runtime evidence fusing into one exportable, auditor-ready artifact. This was the demo people pulled colleagues over to watch.
Every AI supply chain runs through vendors nobody controls. Walking TPRM teams through how the Trust Loop covers those too was the conversation that kept restarting.
The whole back wall was the AI Trust Loop — Discover, Observe, Govern, Secure, Prove, running as one continuous motion. It turns out that is a very easy thing to talk about in a room full of auditors.
AT&T Secure Connections is the next stop — Sept 30 – Oct 1, 2026 in Dallas, TX. Book time with the band before the floor fills up.
We use essential cookies to run this site, and — only with your permission — analytics and marketing cookies to improve it. You're the hero here; you stay in control. Privacy Policy.